

Overview
Humanos is the Risk Network for AI. AI risk changes every time an agent acts, so Humanos measures it continuously, reduces it with runtime controls, and makes it provable with signed, verifiable evidence. The Humanos API is how your systems take part in that network:- Control risk. Verify every agent action against a user-approved mandate before it executes, and capture human approval at runtime when an action falls outside its scope. See Agent Actions and Collecting Approvals.
- Measure risk. Every approval, verification, and revocation is recorded as a signed event on the credential’s chain: runtime evidence about each mandate and the agent acting under it.
- Build on risk intelligence. Read risk metrics computed from that evidence for your own agents, or for a partner’s agents while they share access with you. See Risk Metrics.
Base URL:
https://api.humanos.tech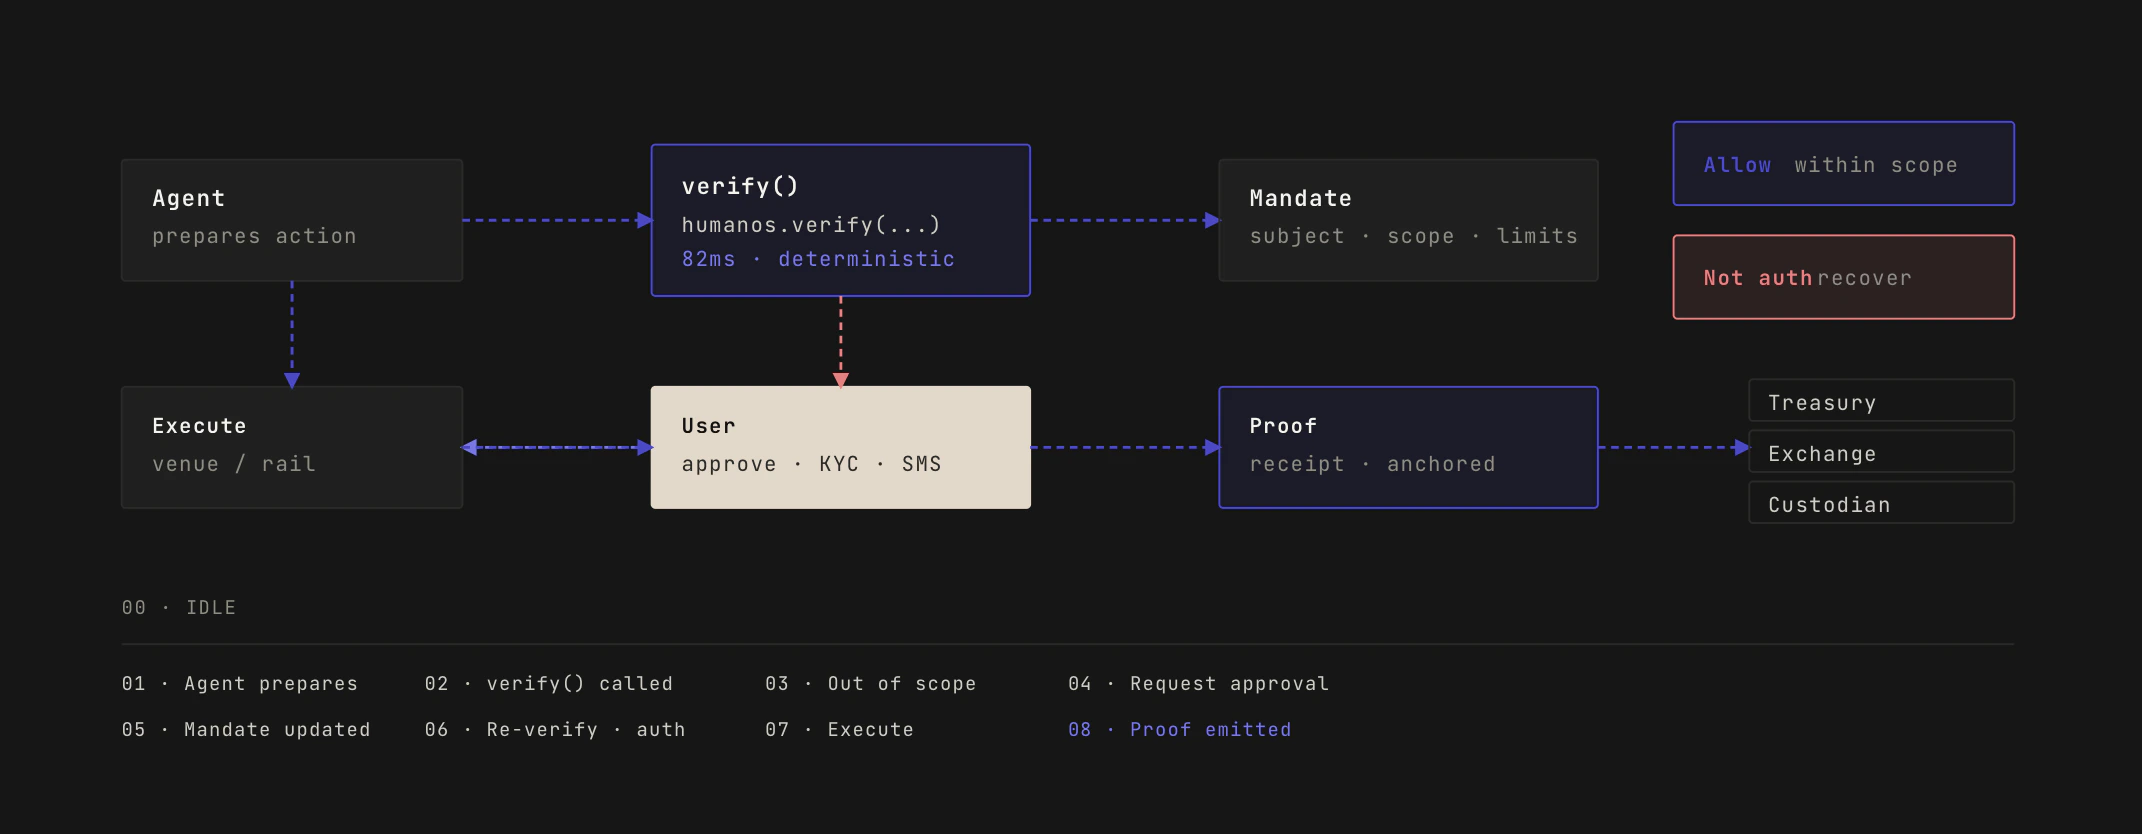
SDKs
Skip the raw HTTP calls. Our official SDKs wrap every endpoint in idiomatic bindings for your stack, including auto-signing and webhook decryption.- TypeScript
- Python
- C#
For the full SDK documentation click here.
Concepts
Lifecycle
A mandate’s lifetime breaks into two flows:- Request and approval happens once. You define an action, request a mandate, and the user accepts or rejects. On accept, Humanos issues the mandate and you persist its ID.
- Issuance and verification happens on every action. The agent issues a fresh VP from the mandate, Humanos verifies it against the agent’s
executionParams, and returns allow or deny.
Audit trail
Every consequential event in a mandate’s lifecycle, whether issuance, approval, verification, or revocation, is persisted as an immutable, cryptographically signed record chained to the credential. Audit Credential Event Chain re-verifies that chain and returns a tamper-evidence report (credentials issued before the v0.2 format have no chain). You get a complete, tamper-evident history without logging anything yourself, and it is the same evidence the risk metrics are computed from.W3C standards
Every entity in the Humanos ecosystem, whether an automated system, an organization, or an end user, is identified by a Decentralized Identifier, or DID, that complies with the W3C DID standard. All authorizations are encapsulated as W3C Verifiable Credentials 2.0, giving each authorization a cryptographic proof, a tamper-evident structure, and a complete audit trail.DID 1.1
W3C standard for verifiable identities with no central registry.
VC 2.0
W3C data model for the credentials every authorization uses.